

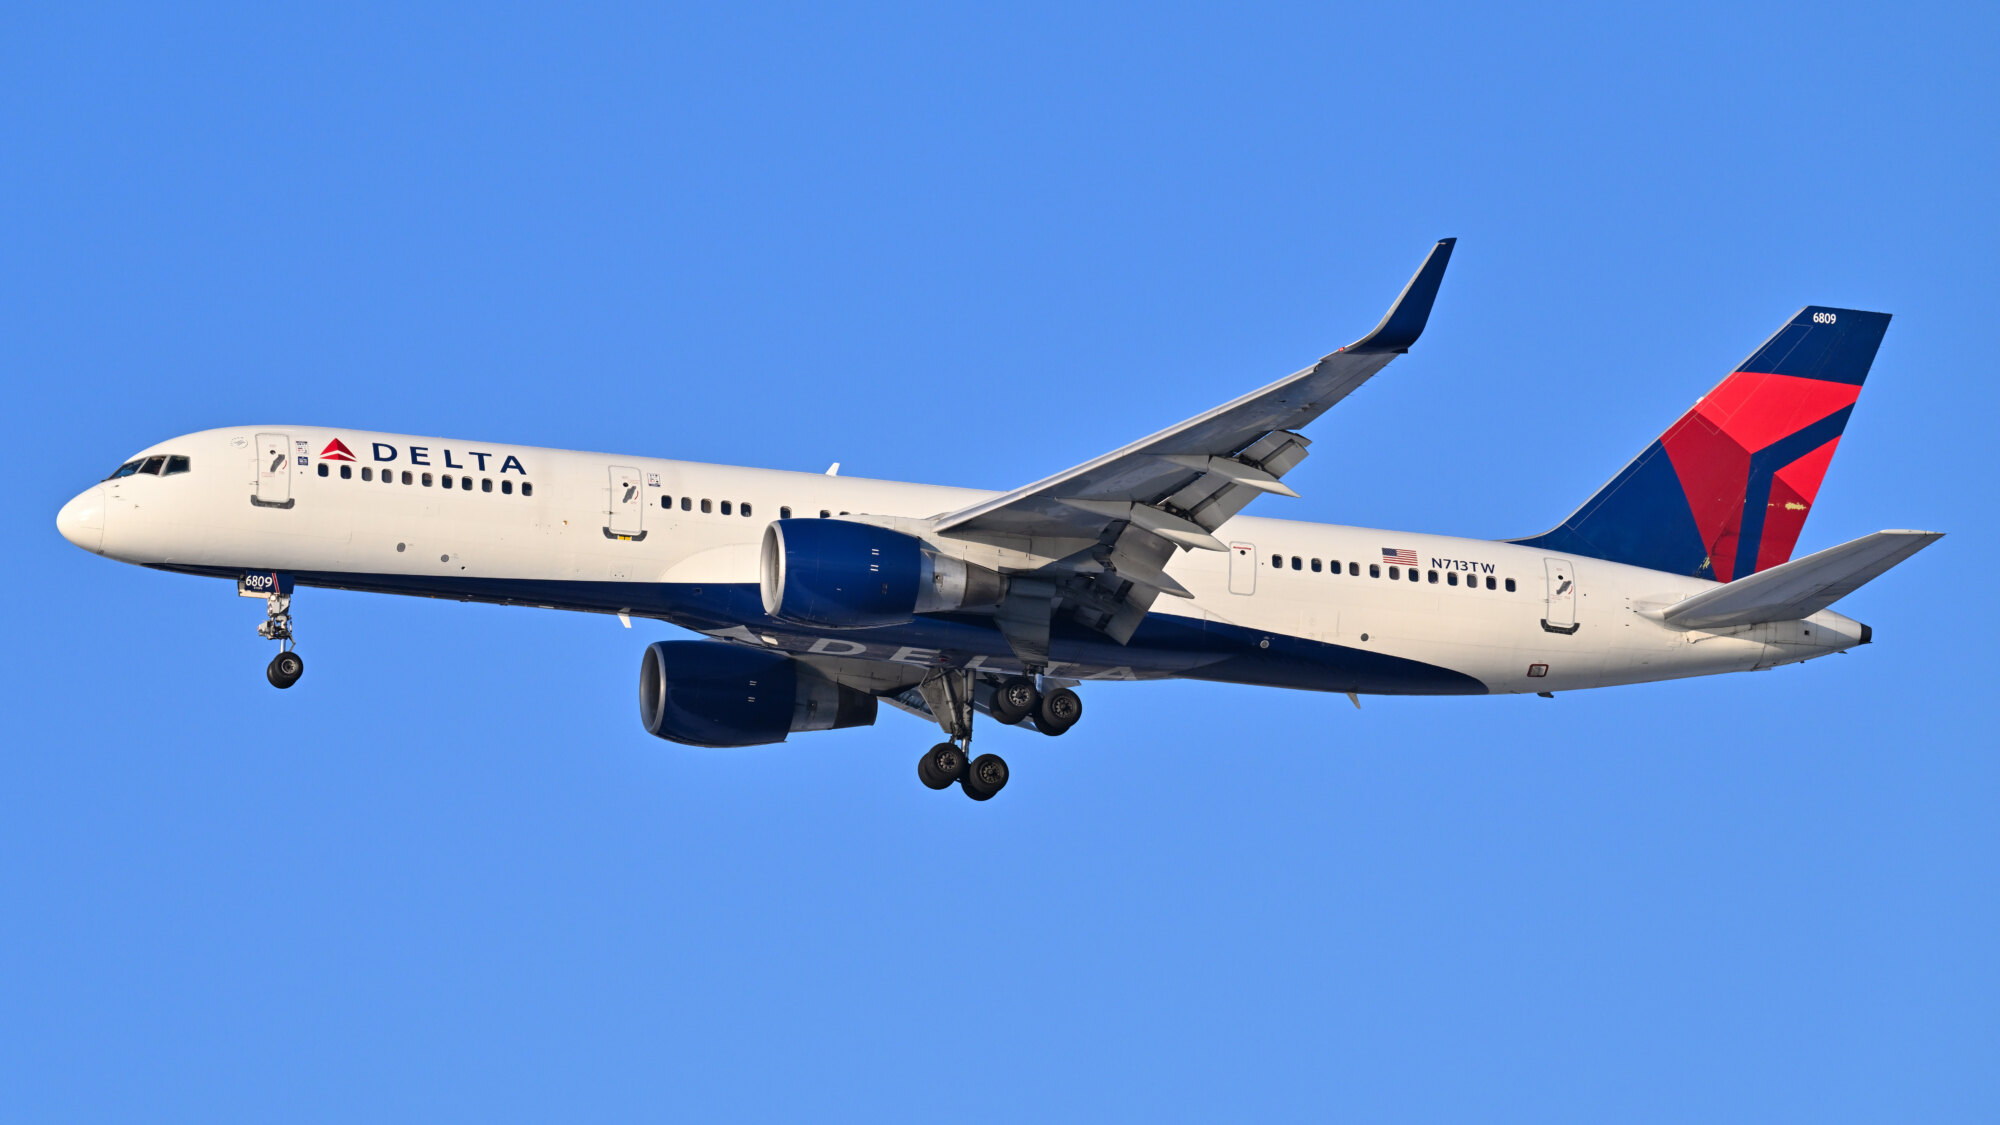
Doctors always advise against driving yourself to medical help, but the captain of a Delta Air Lines flight from L.A. to Boston didn’t have much choice. The steering wheel is on his side. The pilot diverted to Detroit on Wednesday and was the pilot not flying as the Boeing 757 did a brisk descent to Detroit Metro Wayne County, which was right on the track for Boston from L.A. But after the aircraft landed it was up to the captain to take over the controls. “I’m going to taxi the jet to the gate and then I need to go to the hospital,” he said on the ATC tape.
As the first responders dealt with the captain, Delta operations was coming up with a different kind of miracle. There happened to be a spare 757 crew available in Detroit and they strapped in shortly after the ambulance left. The flight was only about 90 minutes late getting to Boston. There has been no word on the captain’s condition.

And Airbus wants to go to one-pilot commercial airliners. :sigh:
I think that pilot incapacitation is one of the unbeatable arguments in favor of zero-pilot airliners. Driverless taxis are undeniably far, far safer than human-driven taxis. It will be exactly the same for airliners when that day arrives.
I think you have it backwards. When all those Waymos stopped in the middle of the streets of San Francisco, the passengers got out and walked. Not exactly an option for airplane passengers.
I don’t like any machine that has the ability to take the controls away from the pilot or driver. Fly by wire can and does do exactly that. Cars can be driven remotely in this manner and airplanes can do the same thing.
So with the Waymo system failure, you’re saying that the system reverted to a fail-safe mode and nobody was hurt, nor was there damage to property? Right? Okay, got it.
Long before we were born, the printing press was thought to herald the end of society. Later, the Jacquard weaving loom was said to be the end of economic order. Then slide rules were seen by many as the ultimate tool to steal intelligence. And after that, telephones were going to destroy nations. Commercial radio transmissions were later thought to be doing the job. Then TV. Yet later, many held up the electronic calculator as the ultimate statement of stupidity. Then it was personal computers. And video game consoles. And smart phones. Now it is gene therapy, genetic modification, AI, and driverless vehicles.
Those that quake in fear of the future and see only problems are those that are always left behind by history. And that is as it should be.
All it would take is a hostile cyber attack from a foreign enemy, to bring down every airliner in the sky simultaneously.
Look how fragile infrastructure is already. If one is concerned about a future cyber attack bringing down a bunch of ‘planes containing a vanishingly small percentage of the population, then one should first worry about integrated water supplies, networked nuclear power plants, and the rest of it. The vulnerability exists today, and our leadership must consider it to be a very acceptable risk since no meaningful action is taken to mitigate it. Oh, wait, I did notice additional dog patrols a while ago.
Indeed it is fragile. And you make a very good point about all of the other fragile and vulnerable parts of the system as well. As for our leadership considering it to be an acceptable risk, or how much you believe in it, I’ll let you decide that for yourself. But as it stands, neither side trusts the other to even carry out free and fair elections. So you have more trust in them than they have in each other, regardless of which party you support.
By “leadership” I was talking generically about The System. The vulnerabilities are systemic and have existed for several decades. Politicians tend not to be well-educated, nor (with a few notable exceptions) particularly intelligent, in my admittedly subjective opinion. They display tremendous difficulty appreciating the repercussions of actions, and likewise inaction. And so it goes.
I avoid party politics like the maggot-filled, open sore that it is. Reducing a discussion to rage, hatred and party politics, while in vogue, serves nobody except those that circle like hyenas, and certainly doing so does not serve the proles who who live and die by politicians’ ofttimes serendipitous successes and their predictable mistakes.
Or a suicidal pilot… or 2, 3 ? Or one that enters the wrong waypoint, or doesnt intervene quickly enough when acceleration isnt where it should be ? Or controllers that go home 1h early ? And so on and so on. There are arguments both ways. Take away the self-interests of pilots and controllers, let pax safety be the primary goal, and lets derermine what works best. Surely we hv to acknowledge that as tech has progressed, pilots have more and more become a weaker part of the chain. Pax deserve what is best for them. Read the NTSB reports…
An enemy cyber attack could hit every fly-by-wire airplane in the sky simultaneously. Hopefully every pilot in the sky doesn’t become suicidal all at the same time as you have suggested about 2 or 3 pilots. Although many have postulated that the Covid vaccines in addition to being population reduction devices, are also an operating system that becomes a remote control device for humans, much like remote controlled drone airplanes and cars. The technology definitely exists to do that and Hollywood has even made futuristic movies to tell us about remote controls causing mass suicides. So I don’t discount your point about suicidal pilots, but let’s remember that either scenario involves high tech and remote control causing the problem.
I agree with Rob. We are not there yet, but when the weakest link in the chain is the human in the cockpit, the solution won’t be to add more humans, it will be to remove them. Problem solved!
When everything goes to hell and the automation starts doing uncomanded or inappropriate behavior the LAST LINK IN THE CHAIN is a competent person directly on the spot to take immediate control and corrective actions!!!!!!!!!!
Yes, I agree. But the horse is already out of the barn on that one, at least in fly-by-wire airplanes. The pilot has no way to directly control the airplane himself. He has a tiny, electronic joystick mounted where he can only use one hand to send electronic signals to the flight controls. If other electronic signals take that control away from him, the pilot simply becomes another passenger with a special view that allows him to see the destination of the airplane before all the other passengers do. Whether that is a tall building, an ocean, an airport, or another country far from where he planned to be. He gets to see it first. But when there is an electronic cyber hijacker, the pilot is no longer determining the destination of the airplane.
Let’s hope there’s enough redundancy in the systems that the human pilot can recognize that something has gone astray and pull the reins in before the situation gets too far out of hand.
“Ladies and gentlemen, we’re about to begin our descent… our descent… our descent…”
If we ever have this scenario in the future, our successors might call this event “controlled flight into terrain,” and abbreviate it as CFIT. I am so glad that humans prevent this from happening now.
True. A computer can probably do a better job keeping an airplane from colliding with terrain, especially, non professionals, but how do you get rid of the humans that program the computers? In nearly 19000 hours of flying, I have never had an accident. But I have had lots of computer failures.
And I can recall numerous times landing in turbulence and crosswinds where I had to turn off a wonderful autopilot because it just couldn’t anticipate what the winds and turbulence would do next.
Somewhere else in the thread, someone said that we’re not there yet. This is accurate; we are not. But for every automation error caught by a human, there are errors that are prevented by automation. These are mostly not publicized and often not even recognized.
I can imagine a scenario where companies like Natilus will introduce automated cargo flights, and there will be failures, perhaps even some deaths. The errors will be investigated and corrected, and society will accept the cost/benefit ratio, as it always does. Just like, say, train travel. In the 1800s, train travel could be quite dangerous. Consider the Versailles incident. User testing found the problems, they were corrected, and society moved on. Nobody thinks about it now.
The same goes for pressurized jet turbine aircraft. New technology was commercialized, some people died, the problems were identified and addressed, and a while later it was like it never happened. Most airliner passengers today don’t even know about the deaths of the past that contributed to increased safety today.
X-rays are now considered routine. My dental practice does them without thinking. The computer takes care of the dose, and it incorporates the learning resulting from the deaths caused by the Therac-25 medical X-ray machine in the 1980s The important thing for people today is that the knowledge those deaths gave us means that we are all at much lower risk of death via X-ray overdose.
I am not saying that people dying due to unidentified issues encountered on the way to mass commercialization is a good thing. I am just saying that it does result in ultimately adequate safety and society always accepts the cost, with the odd exception. (Thalidomide, anyone?)
I wonder if a computer gets scared or becomes significantly more alert and protective when it senses a particularly dangerous or strange new situation, or if it just keeps doing what it is trained to do by programmers who don’t know how to fly? I think we all know the answer to that question.
Apologies for the delayed response.
I know nothing about cognitive science, but this is the internet and my ignorance is not going to prevent me from speculating.
What is “scared”? Is it “dread” where, I posit, that your subconscious is aware that something is wrong or that a risk exists, but that understanding has yet to be transferred to your conscious mind? Dread, I suspect, is the subconscious saying, “Be careful while I process this.” Not a problem for software with instantaneous fetch routines.
Or is it “fear”, when our mind is basically saying, “Stop all other cognitive processes and focus 100% of your processing power and sensorary apparatus on this single issue.” Again, not a problem for a computer. Our organic hardware processes information very slowly, but our organic firmware is impressively adaptable. Inorganic by contrast processors are blisteringly quick, but with zero adaptability beyond their scope of validity. Since processing capability is cost-free, in corporate terms, it’s just the (formidable) issue of getting the software right.
So, I see “scared” in terms of algorithmic processing priorities.
And I guess that most programmers do not know how to fly. But those specializing in the relevant fields sure know how systems and redundancy should be implemented. Sure, sometimes today they get it wrong and there is an incident, or worse, due to faulty automation. Just like human controllers or pilots, systems programmers miss implicit malfunctionalities and make errors. But while humans continue to repeat the same operational errors, once a coding error or systems configuration error is fixed, it is usually fixed forever.
Remote piloted Drones crash far more often than piloted airplanes. A pilot sitting in a mobile home out in the desert in front of a bank of computer screens doesn’t have any skin in the game if it crashes.
And the computer only has the experience that the computer programmers give it. They are computer programmers, not professional pilots. So you may say that computers learn as they go. Hey, that’s Great! Do you want those computers to learn from the airplane that crashed with you on board? And how do you even know that the computers are not using trial and error to figure why the last few airplanes crashed? This all assumes that computers don’t decide that the human race needs to become extinct in order for AI to take over. It also assumes that there isn’t a software glitch nobody anticipated.
I’m ordinarily a single pilot kind of guy, but an airliner needs 2 guys up there. The one pilot they plan to put up there doesn’t really fly it anyway. He just monitors the drone.
No word on the condition of the captain. And guess what? If he was having a blood clot/coronary or other Covid vaxxx related issue, there won’t likely be any further word on this captain.
Covid vaccine issue , Oh my let’s stir and bring that pot to a roaring boil.
no No NO !!! Let’s not
Absolutely. Gotta keep it quiet so an unsuspecting public won’t get wise to the plot next time they try a population reduction and control measure. Shhhhhh!
In another incident within the past year, the captain of an ATI 767 became unresponsive and the F/O was basically solo on his decent, approach and landing to Anchorage.
‘Dangerous’, ‘Scared’, ‘Strange’ are human constructs that Autonomous Intelligence has no use for. Just as Stewardess evolved to a more fitting description of Flight Attendant, AI should be more accurately called Autonomous Intelligence once it evolves out of its infancy.
Since AI is naturally efficient, it will eventually figure out humans are very inefficient and are AI’s greatest competitor for its lifeblood – ENERGY. Energy in all things, aviation included, will be the only state worth consideration when it comes to man vs machine and is being shown to be true already. What would an intelligent being do to its greatest threat if it were truly intelligent?
It’s long but a very interesting read of Bill Gates’ recent essay: https://www.gatesnotes.com/a-turbulent-ai-era-and-critical-choices-to-make